Businesses store sensitive information across cloud platforms, internal networks, business applications, employee devices, and databases. Without proper controls, users or systems may gain access to information they do not need.
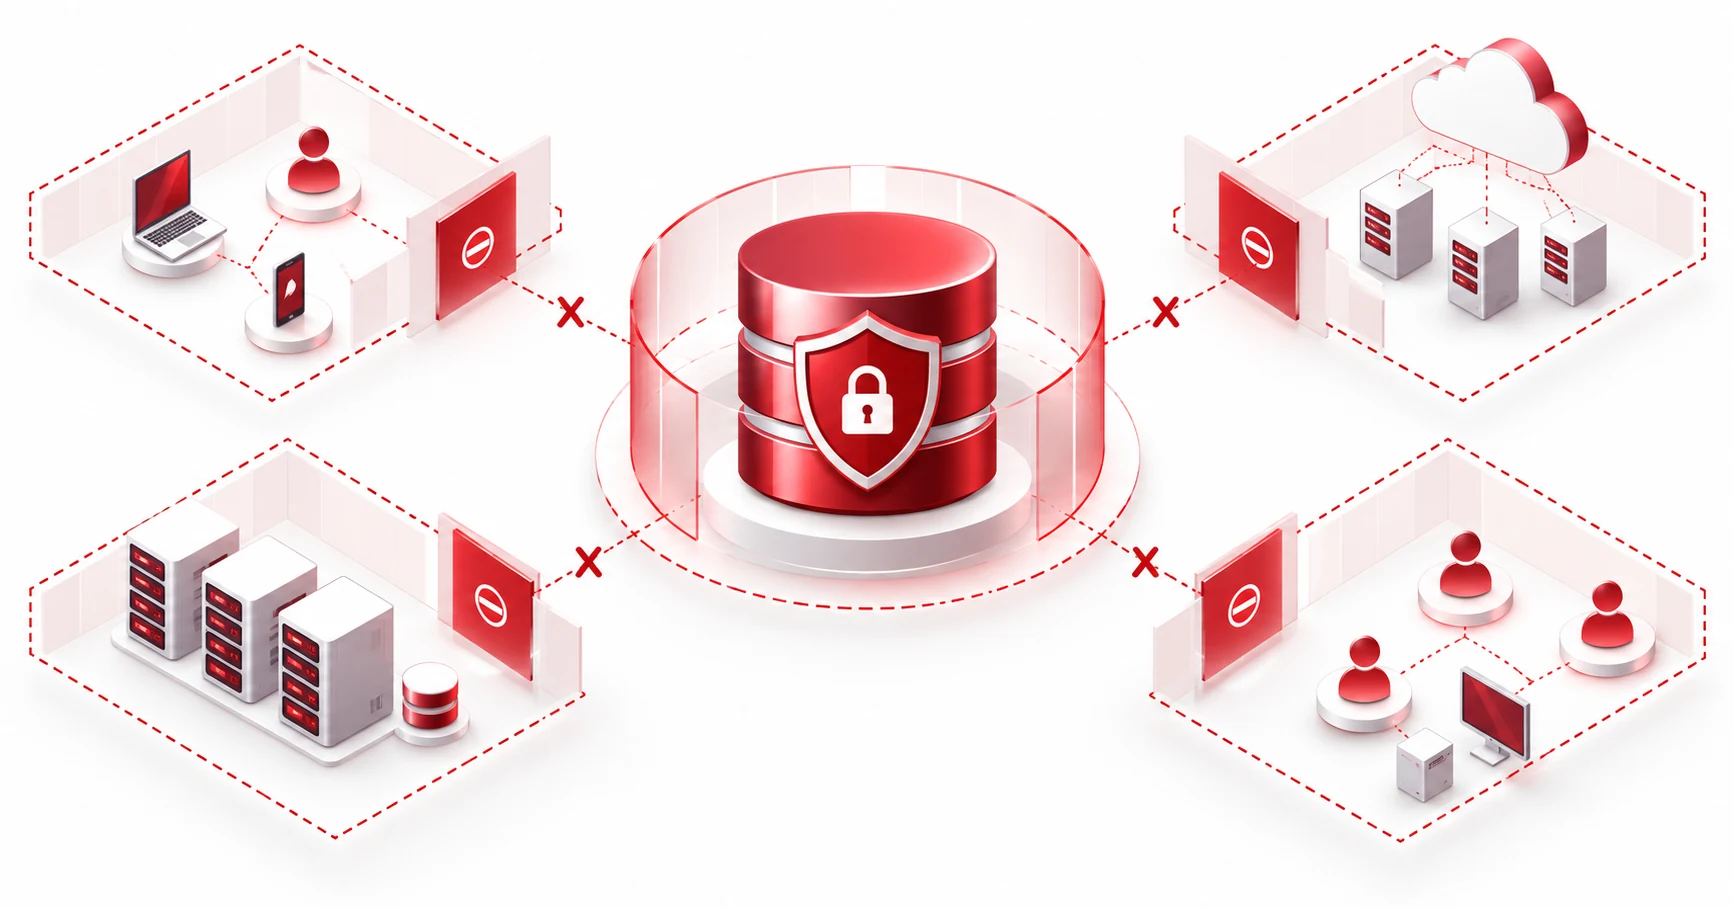
Data isolation helps reduce this risk by separating sensitive information, systems, users, or workloads and controlling how they interact. When implemented properly, it can limit unauthorized access, reduce the impact of a security incident, and provide stronger protection for important business data.
Key Takeaways
- Data isolation limits access between users, systems, workloads, or datasets.
- Access controls, segmentation, encryption, and separate environments can enforce isolation.
- Strong isolation can reduce data exposure if one account or system is compromised.
- Cloud environments often use logical boundaries to separate tenants and resources.
- Isolation controls should be reviewed as users, systems, and business needs change.
What Is Data Isolation?
Data isolation is the practice of creating boundaries between information, users, applications, systems, or environments so that access is limited to authorized users and processes.
For example, a business may isolate employee payroll records from general company files. Only HR and authorized managers would have access to the payroll data, while other employees would be restricted.
Isolation can be implemented through:
- Access permissions
- Separate networks
- Dedicated storage or databases
- Encryption
- Cloud tenant boundaries
- Separate accounts or environments
Before businesses determine what information needs stronger isolation, it helps to understand how sensitive that information is. Adivi’s data classification guide for small businesses explains how organizations can categorize information based on sensitivity and risk.
Data isolation in cybersecurity should not be confused with database transaction isolation. Transaction isolation is a database concept that controls how simultaneous transactions interact. This article focuses on protecting business information by restricting access and separating resources.
How Does Data Isolation Work?
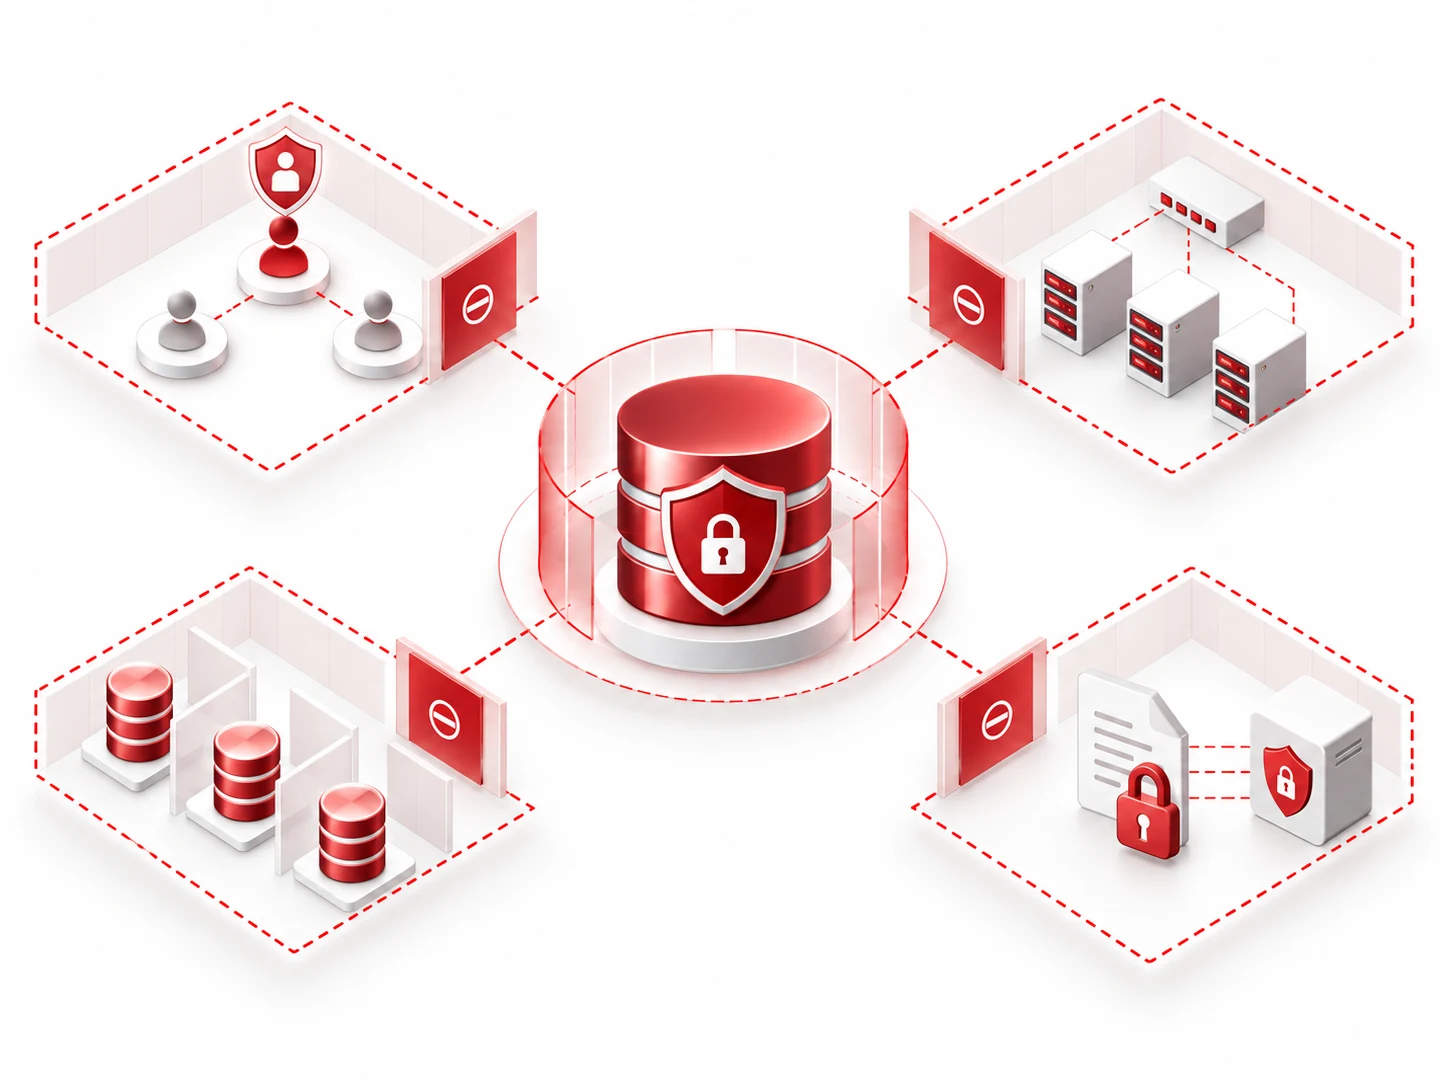
Data isolation can be implemented in several ways depending on where information is stored and who needs access.
Access Controls and Permissions
Access controls determine which users can view, modify, download, or share information.
Businesses can assign permissions based on an employee’s role and responsibilities. For example, accounting employees may need access to financial records, while sales employees may only need customer and sales information.
Following the principle of least privilege helps ensure users receive only the access necessary to perform their jobs.
Businesses should also review permissions regularly. Employees may change positions, leave the company, or no longer require access to certain information.
Poorly managed permissions can contribute to accidental exposure. Adivi’s guide on preventing accidental data sharing explains how businesses can reduce these risks.
Network Segmentation
Network segmentation divides a business network into smaller sections.
Instead of allowing every device and system to communicate freely, businesses can create boundaries around important resources.
For example, a company might separate:
- Employee devices
- Guest Wi-Fi
- Financial systems
- Servers
- Security cameras
- Production environments
If one area of the network is compromised, segmentation can help limit access to other areas.
Separate Storage or Databases
Businesses can also isolate information by storing sensitive data separately.
Highly confidential customer information, financial records, employee files, or restricted business documents may be kept in separate databases, storage locations, or systems.
Separating sensitive data can make it easier to apply stricter access rules without placing the same restrictions on every business file.
Encryption
Encryption protects information by converting it into a form that cannot be easily read without the appropriate key.
It can protect data both while it is stored and while it is transferred between systems.
Encryption alone does not create complete isolation, but it provides another layer of protection if unauthorized users gain access to storage or intercept data.
Tenant Isolation in Cloud Environments
Cloud services often support multiple organizations on shared infrastructure.
These organizations are commonly referred to as tenants.
Cloud platforms can use logical boundaries, identity controls, authorization policies, separate databases, or dedicated resources to prevent one tenant from accessing another tenant’s information. The exact level of separation depends on the architecture and security requirements.
Businesses using cloud platforms still need to configure permissions and security controls correctly.
Why Data Isolation Matters
Data isolation reduces unnecessary exposure and creates boundaries around sensitive systems and information.
Prevents Unauthorized Access
Employees should not have unrestricted access to every file or system within an organization.
Isolation helps businesses limit access based on business requirements.
For example, payroll records can be restricted to HR, while confidential client files may only be available to employees assigned to that account.
Limits the Impact of Security Incidents
Isolation can help reduce how far an attacker or malicious program can move through an environment.
If sensitive resources are properly separated, compromising one device or account does not automatically provide access to every other system.
Isolation therefore works as one part of a broader defense-in-depth strategy.
Protects Sensitive Business Data
Businesses may store customer records, payment information, employee files, financial information, contracts, credentials, and other sensitive data.
These types of information often require stronger protection than general business documents.
Data isolation allows organizations to apply additional controls where they are most needed.
Supports Data Protection Policies
Isolation can support broader security practices by helping organizations define who can access information and where it can be stored.
It often works alongside technologies such as encryption, identity management, monitoring, and data loss prevention.
Data Isolation vs. Data Segregation
Data isolation and data segregation are closely related, and the terms may overlap depending on the technology being discussed.
Data segregation generally refers to organizing or separating information into distinct groups based on factors such as sensitivity, department, customer, or purpose.
Data isolation focuses more specifically on enforcing boundaries so that users, systems, or workloads cannot access information outside their authorized area.
For example, a company might segregate information into:
- Public
- Internal
- Confidential
- Restricted
It could then isolate restricted information by placing it in a separate system and allowing access only to specific employees.
In practice, segregation helps determine how information should be separated, while isolation helps enforce that separation.
Data Isolation in Different Environments
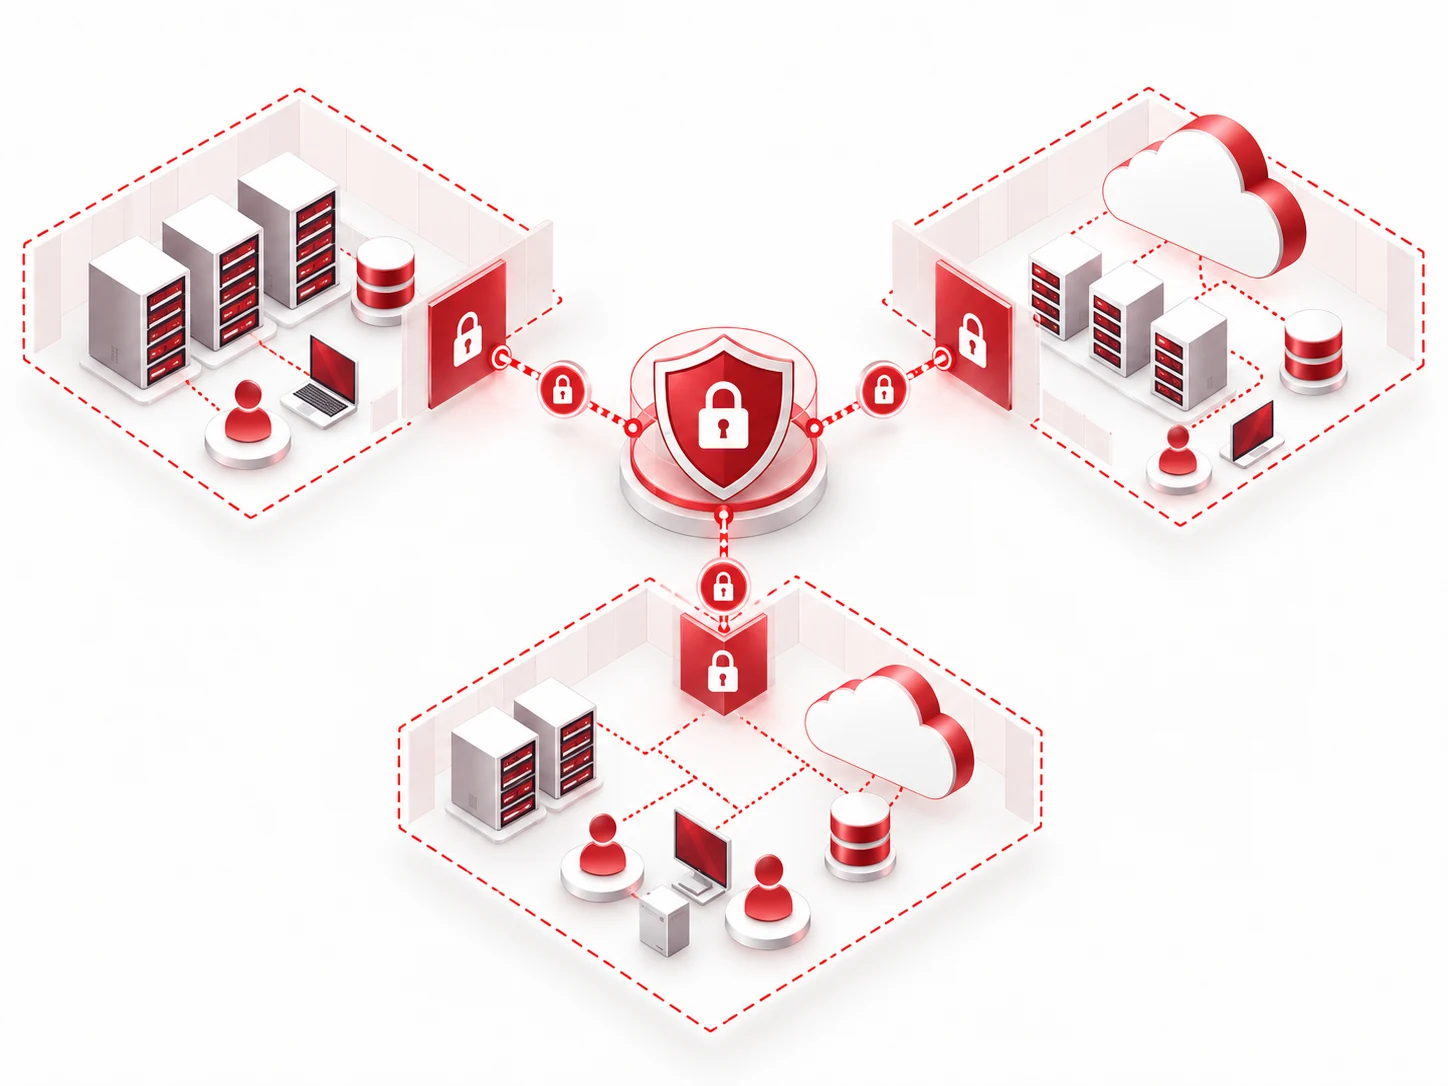
Businesses may need different isolation methods depending on how their technology is structured.
On-Premises Environments
Businesses managing their own infrastructure can isolate data through:
- Network segmentation
- Firewalls
- Separate servers
- Dedicated storage
- User permissions
- Physical security
The organization is responsible for maintaining and monitoring these controls.
Cloud Environments
Cloud environments may use logical or physical separation depending on security and operational requirements.
Businesses can strengthen isolation through:
- Identity and access management
- Role-based permissions
- Separate cloud accounts or subscriptions
- Private networks
- Encryption
- Separate storage resources
- Tenant-level controls
Different workloads can require different degrees of separation. Some may share underlying infrastructure while using logical security boundaries, while more sensitive workloads may require dedicated resources.
Hybrid Environments
Hybrid environments combine local infrastructure with cloud services.
This can make isolation more complex because businesses need consistent controls across multiple environments.
Strong identity management, network segmentation, encryption, monitoring, and clearly defined access policies can help maintain appropriate separation.
Adivi’s guide to hybrid cloud security covers additional considerations for protecting information across public, private, and on-premises systems.
Best Practices for Implementing Data Isolation
Effective data isolation starts with understanding what information the organization has and who needs access to it.
Businesses should:
- Classify sensitive data. Identify which information needs stronger protection.
- Follow least privilege. Give employees only the access required for their responsibilities.
- Separate critical systems. Avoid allowing unrestricted communication between every device and application.
- Use multi-factor authentication. Add additional protection to accounts that access sensitive resources.
- Encrypt sensitive information. Protect important data in storage and during transfer.
- Review permissions regularly. Remove outdated or unnecessary access.
- Monitor activity. Watch for unusual attempts to access sensitive systems or information.
- Document access policies. Clearly define how employees and third parties should handle restricted information.
These controls should form part of a broader cybersecurity strategy. Adivi’s guide to cybersecurity best practices for business provides additional steps for protecting systems and data.
Common Data Isolation Challenges
Data isolation can improve security, but poorly planned controls can create management and operational problems.
Common challenges include:
- Giving employees excessive permissions
- Maintaining access controls across multiple platforms
- Managing third-party and vendor access
- Applying consistent rules across cloud and local environments
- Separating sensitive information without disrupting workflows
- Identifying outdated accounts and permissions
- Balancing stronger security with employee productivity
Isolation should therefore be reviewed regularly rather than treated as a one-time configuration.
As businesses add employees, applications, cloud platforms, and new locations, access requirements can change.
How Adivi Helps Businesses Protect Sensitive Data
Data isolation works best as part of a broader security strategy.
Businesses need to understand where their data is stored, determine who should have access, configure security controls, monitor systems, and regularly review permissions.
Adivi’s managed IT services can help businesses manage technology environments, strengthen access controls, maintain systems, and reduce security risks.
A structured approach can help organizations protect sensitive information without making everyday technology unnecessarily difficult for employees to use.
Final Thoughts
Data isolation helps businesses control how information, systems, and users interact.
By separating sensitive resources and limiting unnecessary access, organizations can reduce data exposure and limit the potential impact of compromised accounts, devices, or applications.
Access controls, network segmentation, separate storage, encryption, and cloud tenant boundaries can all contribute to stronger isolation.
The right approach depends on the organization’s systems, data sensitivity, security requirements, and business operations. Regularly reviewing these controls helps ensure isolation remains effective as the business changes.
Frequently Asked Questions
What is data isolation?
Data isolation is the practice of separating data, systems, workloads, or users and restricting access between them. It helps ensure that sensitive information is only available to authorized users and processes.
Why is data isolation important?
Data isolation can reduce unauthorized access, limit data exposure, protect sensitive information, and reduce the potential impact of a security incident.
How is data isolated in cloud computing?
Cloud environments can use identity controls, tenant boundaries, separate accounts, network segmentation, encryption, and dedicated or logically separated resources to isolate information.
What is the difference between data isolation and data segregation?
Data segregation focuses on separating information into different groups or categories. Data isolation focuses on enforcing boundaries that prevent unauthorized users, systems, or workloads from accessing those groups.
What are common methods of data isolation?
Common methods include role-based access controls, network segmentation, separate storage or databases, encryption, dedicated environments, and cloud tenant isolation.
Is data isolation the same as database transaction isolation?
No. Database transaction isolation controls how simultaneous database transactions interact. Data isolation in cybersecurity focuses on separating information, systems, users, or workloads to control access and reduce security risks.